Key takeaways
- Tier 1 banks allocate up to 70% of their annual AML budgets to manual L1/L2 alert processing.
- Rule Decay is the structural condition where expanding, static rule sets yield diminishing detection capability and inflate false-positive rates.
- ThetaRay's detection is a fused ensemble of thirteen algorithms, wrapped in three governance layers, with a separately patented attribution method (US 12,531,885).
- Kaufman Rossin completed an independent validation of ThetaRay's AML Transaction Monitoring and OFAC Screening modules, finalized in August 2025.
- A Tier-1 EU banking group reached production go-live with Ray in ~12 months and signed its Phase 2 expansion 16 days later.
Executive summary
Legacy transaction monitoring systems (TMS) in Tier 1 financial institutions are collapsing under the weight of Rule Decay: a structural condition where expanding, static rule sets yield diminishing detection capabilities, inflate false-positive rates, and consume hundreds of millions of dollars in operational expenditure (OpEx). Adding more rules is no longer a sustainable proxy for improving effectiveness.
As global supervisory bodies transition from static checklist validation to evaluating financial crime programs on demonstrable regulatory effectiveness, Tier 1 institutions face a stark choice: continuously expand manual Level 1 and Level 2 investigation teams, or re-engineer the underlying mathematical architecture.
Co-authored by a former Tier 1 banking compliance transformation executive and a chief AI scientist, this white paper outlines the economic, technical, and regulatory blueprint for transitioning from static rules to an integrated unsupervised machine learning detection and agentic AI investigation operating model.
The macroeconomic crisis of legacy compliance architecture
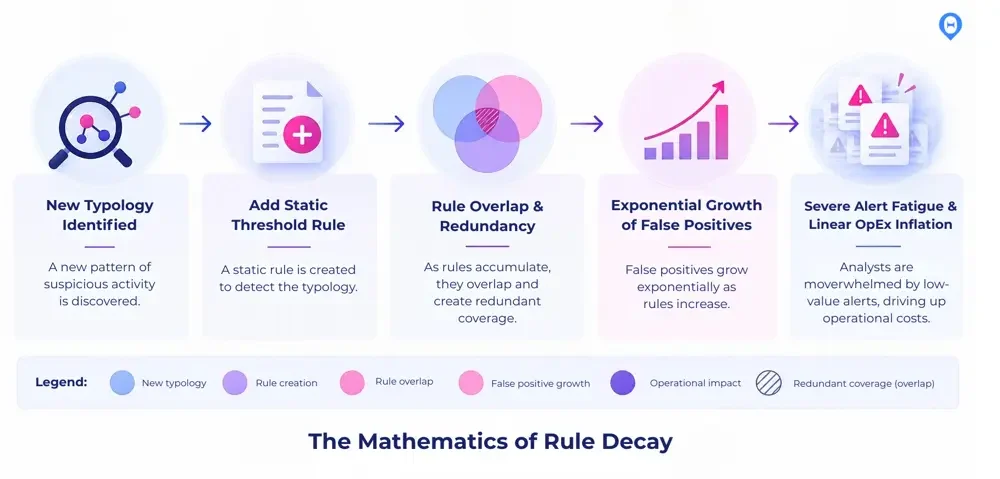
The mathematics of Rule Decay
For two decades, financial institutions have managed emerging typologies by stacking static, threshold-based rules atop legacy architectures. This approach suffers from mathematical decay: as the number of rules increases linearly, the volume of false-positive alerts expands exponentially due to overlapping parameters, redundant flags, and static thresholds that fail to adapt to changing transactional context.
The OpEx and customer churn crisis
70%
of Tier-1 banks' annual AML budget is allocated to manual alert processing
84%
of banking customers would switch FIs following an AML failure
87%
of UK customers would switch FIs following a sanctions failure
Tier 1 banks allocate up to 70% of their annual anti-money laundering (AML) budgets to manual L1/L2 alert processing. Human analysts spend the majority of their time aggregating data, taking screenshots, and verifying false positives, essentially paying human capital to remediate system noise rather than investigate genuine financial crime risk.
Beyond operational cost, this legacy approach creates severe commercial exposure. According to a recent industry report on consumer responses to financial crime lapses and compliance friction, 84% of banking customers in the US report they would switch financial institutions following a major money laundering or sanctions failure, while 87% would warn their friends and family to avoid the institution. The findings underscore the fragility of trust in the financial sector. Legacy rules-based architectures create a double-edged risk: they are too rigid for modern consumers while failing to catch sophisticated crime networks.
88% of banking customers in the UK report they would switch financial institutions following a major money laundering or sanctions failure.
The regulatory shift to "real effectiveness" and analyst market consensus
Supervisory regimes globally are dismantling the "tick-box" compliance paradigm:
- FinCEN Congressional testimony and regulatory modernization (July 2026): In her official written testimony before the U.S. House Financial Services Subcommittee on National Security, Illicit Finance, and International Financial Institutions, FinCEN Director Andrea Gacki detailed the Treasury's active shift toward operational effectiveness, risk-based AML/CFT program rules, and real-time fraud information sharing.
- FATF report on information sharing and public-private partnerships (PPPs) (July 2026): The report identifies at least 84 public-private partnerships globally, with 52 surveyed jurisdictions reporting at least one domestic PPP and 18 reporting more than one. It examines key innovations being used to strengthen information sharing and finds that PPPs stand out as permanent, effective instruments for combating money laundering, terrorist financing and proliferation financing (ML/TF/PF) when supported by a robust legal basis, clear governance, and technological innovation.
- Global supervisors and industry analysts: Supervisors are moving toward evaluating whether a bank's system captures novel, complex typologies without creating massive operational bottlenecks, as highlighted in recent compliance analysis on real effectiveness over static compliance checklists.
This regulatory perspective is reflected across independent analyst evaluations.
A defining feature of the 2026 updates of analyst reports is the accelerating maturity of artificial intelligence (AI) tools. Consensus among the analyst community is that vendors are increasingly deploying generative AI in regulated onboarding environments. As a result, it is becoming a delivery layer for scalable lifecycle management.
As Tier-1 banks evaluate vendors with the mandate to meet both regulatory requirements and their Target Operating Model (TOM), centralized and standardized capabilities across the entire institution's footprint become crucial.
The ThetaRay Platform case for analyst validation
The ThetaRay Platform has demonstrated through Tier-1 bank deployments that its AI model can seamlessly ingest massive enterprise data volumes across multiple jurisdictions without creating operational friction. While other vendors struggle, generating thousands of false-positive alerts in high-risk regions such as Brazil, Mexico or Africa, ThetaRay's models have proven to reduce alert volume by over 50% compared to legacy systems, significantly minimizing alert fatigue.
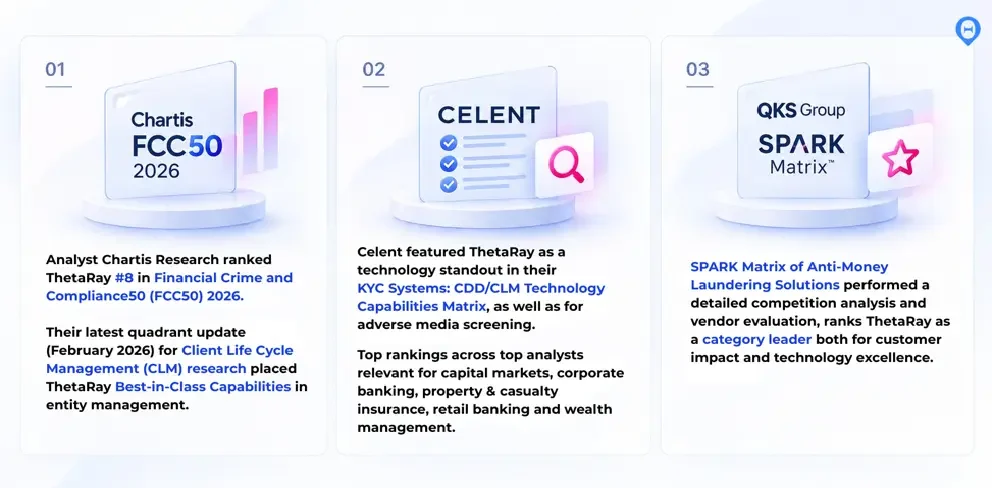
- Chartis Research ranked ThetaRay #8 in the Financial Crime and Compliance50 (FCC50) 2026. Its latest quadrant update (February 2026) for Client Life Cycle Management (CLM) research placed ThetaRay as Best-in-Class for capabilities in entity management.
- Celent featured ThetaRay as a technology standout in its KYC Systems: CDD/CLM Technology Capabilities Matrix, as well as for adverse media screening, with top rankings relevant for capital markets, corporate banking, property and casualty insurance, retail banking and wealth management.
- SPARK Matrix of Anti-Money Laundering Solutions performed a detailed competition analysis and vendor evaluation, and ranks ThetaRay as a category leader for both customer impact and technology excellence.
But beyond recognition in one or two reports, financial professionals must look at comprehensive enterprise scale when evaluating technology. For financial institutions, know your customer (KYC) is a particularly inefficient area of financial crime compliance, often involving intensive manual activity. As financial institutions aim to overcome inefficiencies with advanced technology, new scalable tools such as machine learning and configurable low-code/no-code systems increase operational efficiency in the KYC process.
Re-engineered architecture: from passive detection to agentic execution
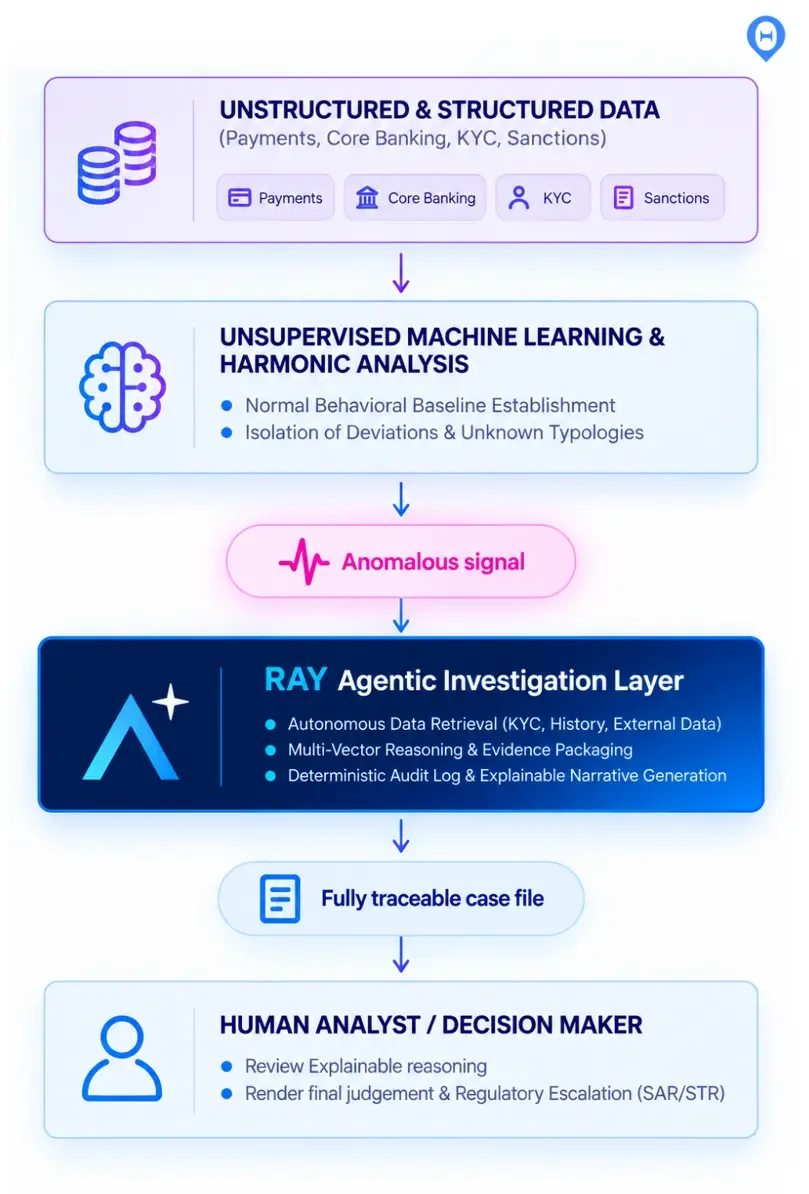
From rule matching to unsupervised behavioral math
Traditional systems ask: "Which transactions match programmed rule sets?"
Advanced unsupervised architectures reframe the operational objective entirely: "What constitutes the normal behavioral baseline across this complex financial ecosystem, and what structural anomalies have emerged?"
Grounded in computational harmonic analysis, high-dimensional signal processing, and matrix decomposition, pioneered through extensive research led by Professor Ronald Coifman at Yale University and Professor Amir Averbuch at Tel Aviv University, this mathematical approach analyzes complex financial data without relying on static thresholds or pre-labeled training datasets.
- Scientific genesis. ThetaRay was founded in 2013 by Amir Averbuch and Ronald Coifman. Averbuch took his PhD in computer science at Columbia (1983), spent 1976-1986 as a research staff member at IBM T.J. Watson, and joined Tel Aviv University in 1987; his fields are applied and computational harmonic analysis, wavelets and big-data processing. Coifman is Sterling Professor of Mathematics at Yale.
- The mathematical lineage. Calderón-Zygmund harmonic analysis led to wavelet packets and "coiflets" (Coifman-Meyer-Wickerhauser). The 2024 AMS-SIAM Birkhoff Prize citation credits Coifman's impact on pure and applied harmonic analysis and the introduction of those tools into modern data science, and names the Coiflet wavelet family specifically. This led to diffusion maps (Coifman and Lafon, ACHA 21(1), 2006; Coifman, Lafon, Lee, Maggioni, Nadler, Warner and Zucker, PNAS 102(21), 2005), which embed a dataset into Euclidean space using eigenvectors of a diffusion operator, so that Euclidean distance in the embedding equals the "diffusion distance" between points. Then came diffusion wavelets (Coifman and Maggioni, 2006) and diffusion bases (Schclar and Averbuch). Prof. Coifman holds the 1996 DARPA Sustained Excellence Award, the 1996 Connecticut Science Medal, the 1999 ICIAM Pioneer Award and the 1999 National Medal of Science. The underlying research program was DARPA/AFOSR/NSF-funded and its lead author holds a DARPA excellence award.
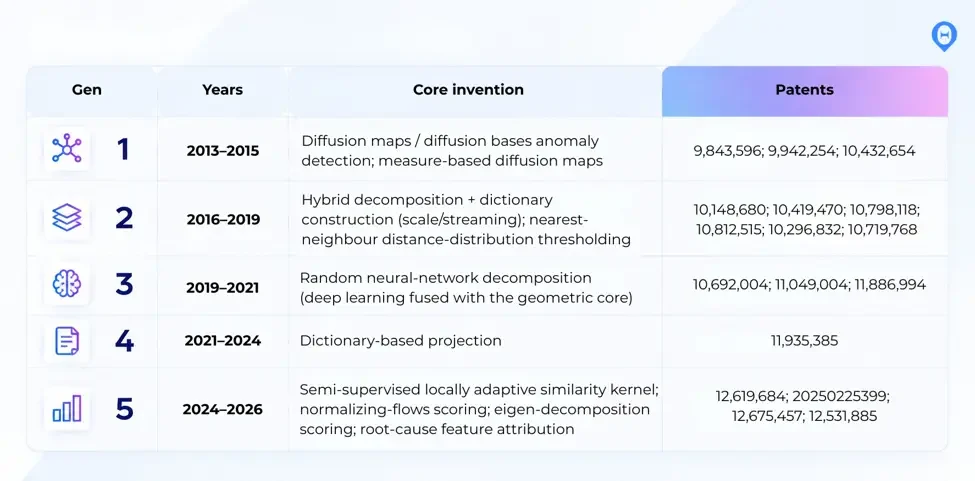
- The original algorithms. As written into the founding patent family ("Anomaly detection in dynamically evolving data and systems", US 9,843,596 / 10,187,409 / 10,333,953): a framework based on diffusion processes and diffusion geometries; eigenfunctions of Markov matrices used to build either diffusion maps (RLDM, per Coifman-Lafon 2006) or diffusion bases (AADB, per Schclar-Averbuch), optionally with random projections; local similarity modeling to self-organize traffic data; diffusion coordinates assigned to each newly arrived data point without recomputing the embedding as new data streams in; and total computation time scaling linearly with data size. Two of these properties are the commercial crux: streaming out-of-sample extension and linear scaling.
- The pivot. Early backing came from JVP (seed, June 2013), followed by GE, around the Advanced Analytics Platform. Financial crime then became the whole company: Transaction AML SaaS (transaction monitoring plus sanctions screening), the July 2024 acquisition of Screena for name screening and entity resolution with syntactic, phonetic and semantic matching, and Ray, the agentic AI investigation suite, launched in January 2026.
Supported by more than a decade of dedicated institutional R&D and over $150 million in total growth funding, including backing from major global fintech investors such as Portage, Jerusalem Venture Partners (JVP), and OurCrowd, these foundational algorithms process high-velocity, heterogeneous transaction streams to isolate subtle behavioral shifts and detect novel typologies before criminal networks exploit structural gaps.
Rather than evaluating accounts against arbitrary dollar caps that assume uniform behavior across an entire customer segment, the platform executes granular data segmentation across entity relationships, geographic corridors, product channels, and temporal frequencies.
By breaking the monolithic rule model through granular data segmentation, financial institutions effectively separate high-volume, legitimate commercial payments from complex criminal layering schemes, driving actionable risk detection while eliminating false-positive noise.
13+ years of R&D
- Patents: The Justia record includes 18 US patents assigned to ThetaRay Ltd, granted continuously from 2015 to July 2026, evidence of unbroken R&D.
- Independent assurance: Kaufman Rossin completed an independent validation of the AML Transaction Monitoring and OFAC Screening modules, finalized in August 2025, confirming the governance, transparency and robustness regulators expect of AI compliance systems in regulated environments. Every Tier-1 bank where ThetaRay is deployed has also completed validation successfully.
Closing the loop with agentic AI (Ray)
Detection without intelligent investigation merely shifts the operational bottleneck downstream. As detailed in a recent AI Journal article on how agentic AI is crossing the line from experiment to infrastructure, Tier 1 institutions are moving beyond generic, conversational LLM chatbots toward production-grade, autonomous agents integrated directly into core compliance workflows.
Ray operates as an agentic AI investigation layer directly integrated with the detection core:
- Autonomous execution: Orchestrates multi-system data retrieval across payments, core banking systems, KYC records, and external data sources.
- Contextual reasoning: Evaluates transaction sequences against customer profiles, peer behavior, and historical patterns to identify contradictions.
The "human-in-control" governance framework
Agentic AI does not eliminate human oversight. Instead, it automates repetitive L1/L2 data gathering and initial synthesis, presenting human investigators with complete, explainable case files.
As explored in industry analysis on setting a new standard for agentic AI in financial services, deploying autonomous agents in regulated banking requires moving beyond basic LLMs to embed deterministic safety rails, structured observability, and continuous evaluation into the core architecture. This ensures the system eliminates hallucination risk while maintaining strict compliance with model governance standards.
What makes Ray not a chatbot?
- Ray is an orchestration layer, not a chat window. Ray plugs into any existing AML case manager or core banking architecture as a universal orchestration layer. Rather than merely collecting data, it autonomously executes cross-referencing, reasoning through risk context and multi-step evaluations as a human analyst would. It is proven in production across rival vendors: at the FX institution it unified ThetaRay detection, Casmex and NICE Actimize under one agentic investigation layer without ripping out existing infrastructure. It is an API-first "AI overlay", with no rip-and-replace.
- Autonomous execution with defined workflow steps, not free-form generation. Ray analyzes each alert end to end and produces a full investigation report: gathering case data, evaluating customer and counterparty behavior, checking KYC/profile alignment, assessing jurisdictions and geographies, identifying contradictions and anomalies, correlating historical alerts and past cases, organizing documentation, and recommending next steps.
- Scoped data access. Autonomous evidence collection covers counterparty context, geolocation and OSINT; KYC integrity validation checks that transactional activity matches the declared profile and risk rating; geo-spatial review runs cross-jurisdictional analysis; historical context correlation surfaces "unknown-unknowns" against recurring risk signals; and open-source scanning is controlled, working on verified case data. That is retrieval under governance, not an open-web model improvising.
- Native alignment with detection. Ray understands not just what triggered the alert but why, because it sits on the same engine. A generic LLM bolted onto a rules engine cannot reason about why a geometric anomaly scored the way it did; a bank buying an LLM copilot separately gets narration, not reasoning.
- Explainability and audit trail. Every investigation produces a structured, policy-aligned narrative, a traceable logic trail that removes reviewer subjectivity, and full audit logs created automatically, designed against FCA, FinCEN and Federal Reserve transparency standards. Human-in-the-loop control is retained as required by the EU AI Act.
Why is a financial crime model hard to build in-house?
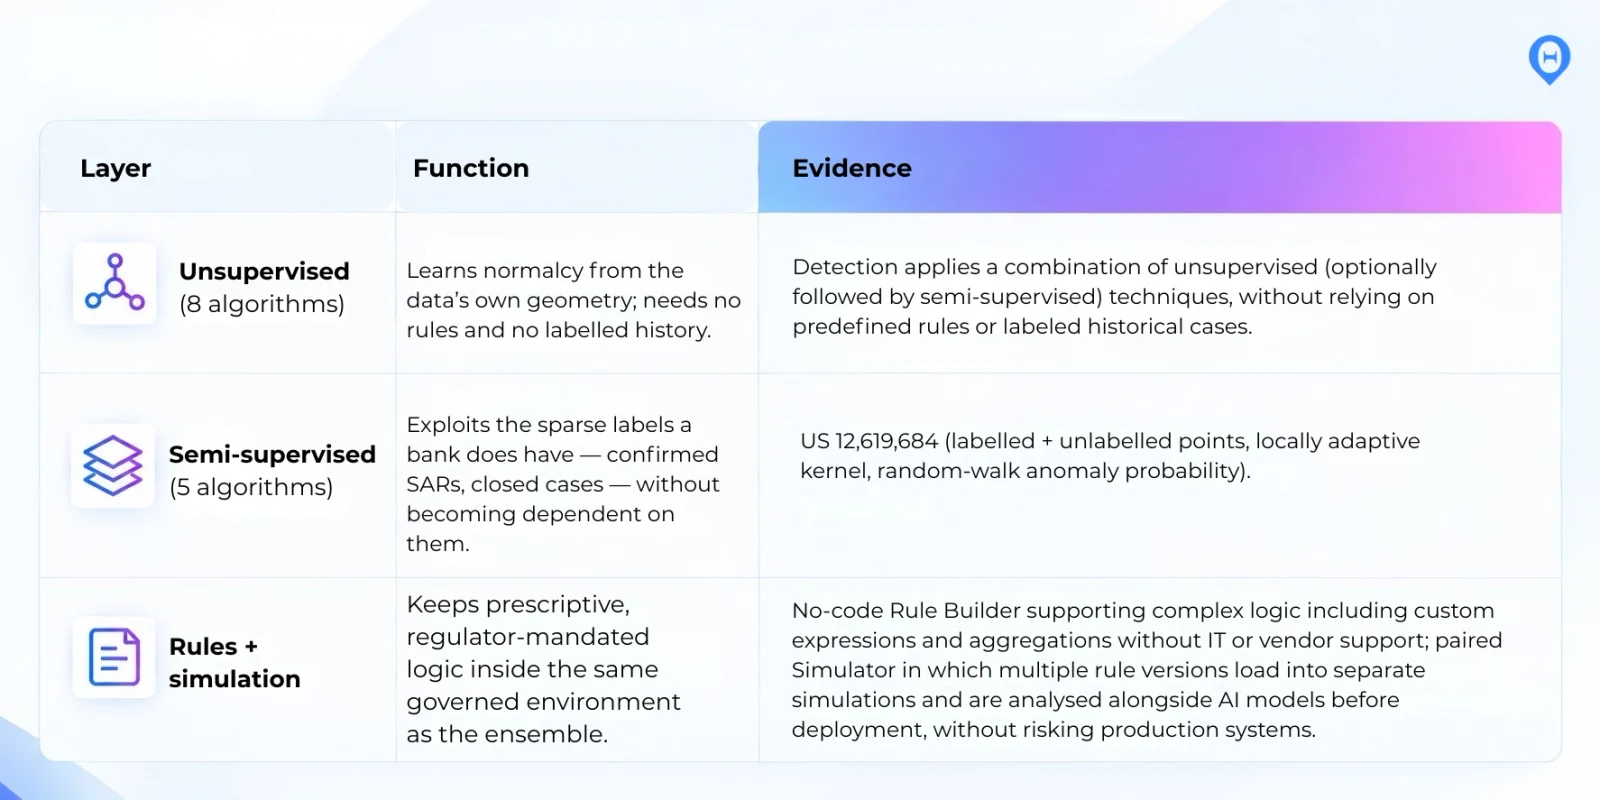
The replication barrier is not a single model. It is a fused ensemble of thirteen detection algorithms, wrapped in three governance layers, made examinable by a separate attribution invention, and calibrated against a cross-institutional data prior. A bank building in-house typically reproduces one algorithm and stalls at explainability.
Why an ensemble, and why it can't be shortcut
Every anomaly-detection algorithm has a characteristic blind spot. A density-based method misses anomalies that sit in dense but wrongly composed neighborhoods. A projection- or dictionary-based method misses anomalies that are ordinary in every individual dimension but impossible in combination. A distance-based method degrades as dimensionality rises.
Criminal behavior is adversarial: it evolves precisely into whatever the deployed detector cannot see. Thirteen detectors with thirteen different failure modes leave far less room to hide than one detector with one, and no amount of tuning a single model reproduces that coverage.
A bank replicating this is not solving one research problem thirteen times. It is solving thirteen different research problems, then solving a fourteenth that is harder than any of them.
The fourteenth problem: fusion
Combining several detectors into one defensible number is where most in-house ensembles fail, for reasons that are unglamorous and unavoidable:
- Score incommensurability. The algorithms emit scores on entirely different scales and distributions: a probability, a reconstruction error, a distance, a likelihood. They must be normalized onto a common footing before they can be combined at all.
- Correlation and double-counting. Detectors that share mathematical machinery agree with each other, so naive averaging silently over-weights whatever the majority family happens to measure. Fusion weights have to account for redundancy between members, not just their individual accuracy.
- Calibration to a single operating point. Compliance needs one threshold with a known alert volume and a known miss profile, not several thresholds. The fused score has to be stable enough that a threshold set this quarter still means the same thing next quarter.
- Attribution through the fusion. When several models contribute, "why did this alert fire?" must resolve to a coherent answer, not a list of several opinions. This is precisely why the attribution patent (described below) matters so much.
Unknown typologies: the mechanism
Three consequences explain unknown-typology detection directly:
- Nothing is specified in advance. The classification of a newly arrived point as abnormal is done by comparing its fused score distribution against a computed threshold. The classification is automatic and unsupervised, without relying on a signature, rules or domain expertise, and the abnormal point is indicative of the unknown undesirable event.
- Normalcy is learned per institution, so knowing the industry's rules doesn't help an evader. The correspondent-banking engagement states the mechanism plainly: by establishing normalcy based on the data, the solution detected abnormal behavior so that only true positives were alerted. The ensemble multiplies this: an evader must look normal to several differently constructed views simultaneously.
- New points score in-stream. Out-of-sample extension is what separates a monitoring system from an academic embedding. Without it, you refit the model to score today's transactions, which is why internal prototypes rarely survive contact with production latency.
Proof that it finds what rules missed:
- Santander UK: The alerts and analytic insights uncovered a human trafficking network through pattern recognition that traditional systems would likely have missed, including high-value payments linked to advertising adult services, with faster escalation to the National Crime Agency. Santander UK's head of transaction monitoring described the effect as making the haystack smaller so they find more needles they might historically have missed. The work was recognized with Best Use of Data for Human Trafficking Detection at the 2024 Digital Transformation Awards.
- Tier-1 global bank (~$1.9tn assets, 3,000+ European branches): The AI identified undetected risk and behavior previously unidentified by legacy systems and, the point that matters most to a Risk Committee, the bank gained approval from its Central Bank and other global regulators on the strength of it.
- New York private bank (~$12bn): The brief was explicitly to optimize prioritization of the existing alert funnel and generate alerts for new criminal typologies. The result was a 50% alert and false-positive reduction while capturing 100% of the SARs filed in the period. Finding new typologies while losing none of the known ones is the hard combination, and it is the combination an ensemble is built to deliver.
- Miami retail bank: The failure mode being displaced is stated directly: rule-based architectures completely missed complex, evolving typologies, leaving the bank exposed to actors who knew exactly how to circumvent standard thresholds.
Explainability is a separate invention, and the ensemble makes it indispensable
ThetaRay solved attribution as its own research problem and patented it. US 12,531,885 ranks the features that caused a specific abnormal behavior, using the gradient of the underlying potential of the diffusion process to identify the direction from an anomaly toward a cluster representing normal behavior, and uses that direction to rate the causal parameters. Note the framing in the patent itself: it assumes the anomalies have already been detected by other methods. In other words, it is deliberately built as an attribution layer that sits over a detection ensemble, exactly the architecture described above.
Operationally, this surfaces as every alert arriving with a holistic view of the transaction, automated context, visual lineage paths and clear rationales for why the activity was flagged, plus human-readable justifications, supporting documentation and confidence thresholds to explain cases and their severity, with audit trails.
Explainability for a banking board of directors: A competent internal data science team can reproduce one anomaly score in a quarter. Reproducing several scores, fusing them defensibly and then generating attribution that is mathematically consistent with the fused score and readable by an examiner is a multi-year program, and the attribution method is patented.
Couldn't we just use an open-source isolation forest?
You can. You then cannot explain it, cannot validate it, and cannot pass an exam on it.
Production feedback loops: outcomes from completed analyses re-enter the system
Every disposition an analyst makes (alert closed as false positive, escalated, SAR filed) can be captured and fed back into the detection engine, so the population of alerts the engine produces next month is shaped by how this month's alerts are actually resolved. The system is not a static model scoring transactions; it is a closed loop in which investigation outcomes become training input.
Why this is the hardest thing on the list to build in-house. A bank can buy or build a detection model. What it almost never builds is the loop, because the loop requires three things to exist simultaneously and stay aligned as the data drifts:
- Outcome capture that is machine-usable. Analyst dispositions have to be recorded in a structured, consistent, reason-coded form, not as free-text case notes that vary by analyst and jurisdiction. Most banks discover their historical case data is unusable as training input precisely when they try to use it.
- An architecture that can consume sparse, delayed, imperfect labels. This is the specific reason the semi-supervised layer exists.
- A safe path from "we learned something" to "production changed". Feeding outcomes back means changing a live control. Without a governed test harness, every improvement is an unapproved model change.
Analyst dispositions are the labels the semi-supervised algorithms consume. That is exactly the shape of a live AML book: a small, growing set of adjudicated cases sitting inside an enormous unadjudicated population. Each closed investigation converts one unlabeled point into a labeled one, and the five semi-supervised ensemble members get sharper.
The loop is described in ThetaRay's own product terms. The platform is documented as connecting human interaction, decision-making and updates from newly available information into a feedback loop so tasks are performed with greater accuracy; adjusting its understanding to new information and responding to new threats faster than human teams or legacy systems; and learning from historical data while continuously adapting to evolving criminal tactics to improve the accuracy of identifying genuine threats.
Ray turns investigation output into structured, reusable evidence. Historically, the feedback signal from an L1 investigation was a close code and a paragraph of prose, nearly worthless as training input. Ray changes the substrate: every investigation produces a structured, policy-aligned narrative, a traceable logic trail, and full audit logs created automatically, and Ray correlates current alerts with historical alerts and past cases to identify recurring risk signals.
Two consequences are worth stating to the board: the loop now receives consistent, structured outcome data instead of analyst-variable text, and the system explicitly reasons over prior case history when assessing a new alert. The previous analyses are consumed at inference time, not only at retraining time.
Changes reach production through a governed gate, not a back door. Feeding outcomes back into a regulatory control is a model change. An improvement derived from last quarter's dispositions can be backtested and evidenced before it changes a single live alert. This is the piece internal builds almost always lack: they produce a better model and then cannot get it approved, because there is no artifact showing what the change does to alert volume and coverage.
The compounding effect. Each institution's loop runs on its own book. But ThetaRay's methodology (the ensemble composition, the fusion approach, the typology library, the configuration patterns) has been refined against feedback from 100+ institutional customers in 40+ countries, more than 1 billion end users, roughly 15 billion transactions annually and $20+ trillion monitored, spanning correspondent banking, payments, trade finance and digital wallets. A new customer inherits thirteen years of accumulated learning about what kinds of feedback matter and how to act on them, then begins generating its own. A bank starting in-house begins its first loop from zero, with no prior about which signals are worth chasing.
Each customer's loop learns from that customer's own data; what transfers across the estate is refined methodology and typology knowledge, not pooled client transaction data. Any board or regulator will ask, and an imprecise answer here creates a data-privacy problem where none exists.
The compounding barrier
Replication requires all of the following at once: eight production-grade unsupervised detectors; five semi-supervised detectors that use sparse labels without depending on them; a fast fusion and calibration method that turns several incommensurable scores into one stable, thresholdable number; a governed rules-and-simulation layer so changes can be evidenced before deployment; attribution that is mathematically consistent with the fused score and readable by an examiner; and a cross-institutional data prior. Twelve out of thirteen detectors and no fusion layer is not a compliance system; it is a research project.
The shortcut is also closed: 15+ granted US patents assigned to ThetaRay, granted continuously from 2018 to July 2026, mean an internal team must design around the specific methods or accept exposure. And the finished product carries an assurance artifact no fresh build has on day one: independent validation of the AML Transaction Monitoring and OFAC Screening modules by Kaufman Rossin, finalized in August 2025, confirming the governance, transparency and robustness regulators increasingly expect of AI-driven compliance systems.
Performance benchmarks and economic impact
Validated Tier 1 customer benchmarks
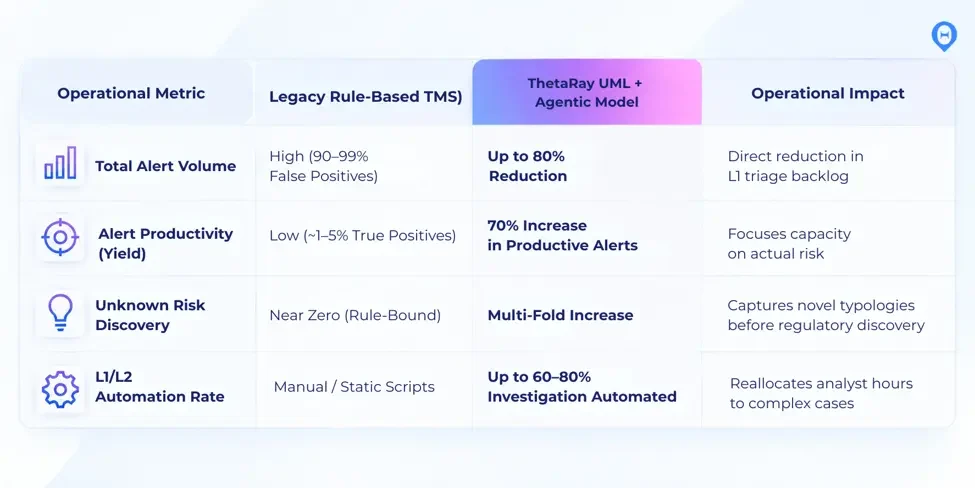
Deploying an integrated unsupervised machine learning (UML) and agentic workflow fundamentally alters compliance economics.
The economics of "build vs. partner" for Tier 1 banks
Internal AI initiatives within Tier 1 institutions frequently encounter multi-year delays, escalating cost overruns, and severe model governance backlogs.
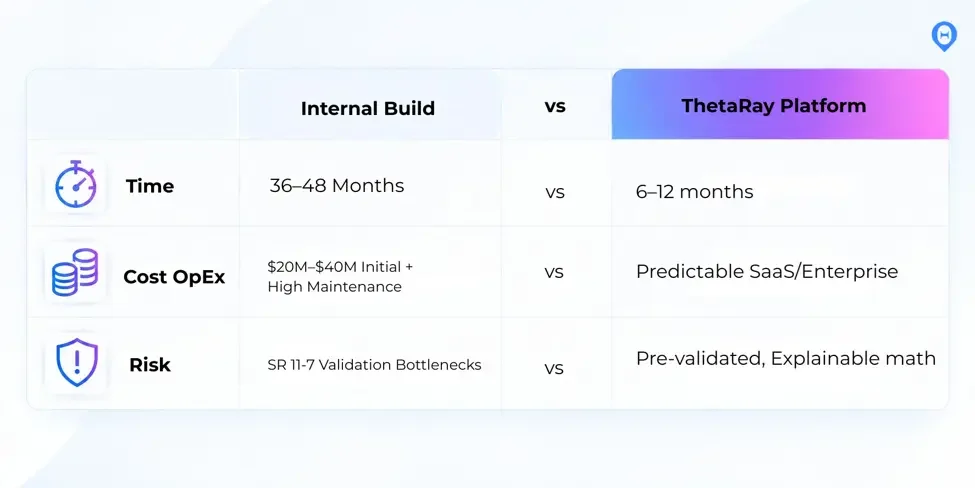
Building an equivalent capability in-house requires assembling specialized data science teams, engineering custom data pipelines, recruiting financial crime experts across global jurisdictions, and subjecting home-grown models to lengthy internal and external model risk reviews.
Partnering with an enterprise provider eliminates this implementation friction. The platform arrives with pre-validated mathematical frameworks that accelerate Model Risk Committee approval. Financial institutions gain immediate audit-ready assurance through independent model validation conducted by Kaufman Rossin, which verified that the underlying AML Transaction Monitoring and Sanctions Screening modules meet strict regulatory expectations for accuracy, governance, and transparency.
What money cannot buy is the cross-institutional prior, and the independent third-party model validation that a bank must commission and re-commission for its own build every cycle.
Governance, explainability, and model risk management (SR 11-7)
Defensibility under Federal Reserve SR 11-7
A primary obstacle to AI adoption in Tier 1 banks is Model Risk Management (MRM) compliance. Unsupervised mathematical models must comply with Federal Reserve SR Letter 11-7 / OCC 2011-12 guidance standards:
- Conceptual soundness: Grounded in peer-reviewed scientific research and advanced harmonic analysis rather than opaque neural network heuristics. This conceptual framework was independently evaluated during the Kaufman Rossin AI model validation, confirming that the platform delivers transparent, robust outcomes aligned with US supervisory expectations and the EU AI Act.
- Outcomes analysis: Clear feature attribution maps precisely why an anomaly was flagged, detailing the underlying behavioral drivers.
- Ongoing monitoring: Automated detection of model drift and data distribution shifts ensures continuous operational reliability.
Audit-ready agentic investigation logs
Every action executed by Ray (data sources queried, logical pathways evaluated, and contextual anomalies highlighted) is documented in an immutable, human-readable audit log. By incorporating a governance-first evaluation framework for agentic workflows, institutions bridge the autonomy-accountability gap, providing internal audit teams and external supervisors with a completely transparent, step-by-step record of the entire investigation lifecycle.
Tier-1 institutions require responsible AI adoption. Only technology partners committed to model risk trust can support systemic banks to deploy agentic AI in FCC operations.
Case study: how a Tier-1 bank built model risk trust to deploy agentic AI in FCC operations
A Tier-1 global banking group (EU) deployed ThetaRay's Ray agentic AI inside its private infrastructure to modernize transaction monitoring investigations while meeting strict Model Risk Management and regulatory requirements.
By combining a deterministic, evidence-backed agent pipeline with 100% human-in-the-loop oversight, the bank achieved production go-live in ~12 months and signed its Phase 2 expansion just 16 days later.
~12 months
to production go-live
16 days
from go-live to signed Phase 2 expansion
100%
human-in-the-loop oversight
The business challenge: navigating model risk and institutional hesitancy
The bank needed to modernize AML investigations without compromising on governance, data privacy or regulatory compliance.
- 95% of alerts were multi-trigger consolidated cases, requiring a complete, unified view.
- All data had to stay inside the bank's security perimeter, with zero egress allowed.
- Compliance and MRM teams required hard proof of explainability and deterministic controls.
The solution: a Phase 1 playbook for governance-first AI
ThetaRay deployed Ray, an agentic AI investigator, running natively within the bank's secure environment. Ray analyzes every alert driver, cross-references customer profiles and historical behavior, and generates audit-ready investigation reports, with the human always in control.
The approach: a six-gate rollout strategy
- Scoped using real alert data.
- Delivered first capability in ~3 months.
- Tuned inside the bank's secure environment.
- Passed formal UAT with 1st and 2nd Line.
- Launched in production (Friends and Family).
- Stabilized and scaled toward full adoption.
Strategic summary for the Board Risk Committee
- The systemic risk: Legacy rules engines expose institutions to severe regulatory and commercial vulnerability by generating massive volumes of low-value alerts, missing novel financial crime typologies, and driving customer churn.
- The strategic impact: By combining unsupervised mathematical anomaly detection with agentic AI investigation workflows, financial institutions can achieve up to an 80% reduction in total alert volume and a 70% increase in true-positive risk detection.
- The bottom line: If a vendor is validated by independent research firms, proven and battle-tested in Tier-1 bank production, and named by CNBC among the World's Top Fintech Companies of 2026, the evidence points to the fact that the explainable AI models used in this approach have demonstrated effectiveness in transforming financial crime compliance from a bloated operational cost center into a scalable, audit-defensible risk intelligence capability.
Frequently asked questions
What is Rule Decay in transaction monitoring?
Rule Decay is a structural condition in legacy transaction monitoring where expanding, static rule sets yield diminishing detection capability. As the number of rules increases linearly, false-positive alerts expand exponentially due to overlapping parameters, redundant flags and static thresholds.
How much of a Tier 1 bank's AML budget goes to manual alert processing?
Tier 1 banks allocate up to 70% of their annual AML budgets to manual L1/L2 alert processing. Analysts spend most of that time aggregating data, taking screenshots and verifying false positives rather than investigating genuine risk.
Why is an ensemble of detection algorithms hard to replicate in-house?
ThetaRay's detection fuses thirteen algorithms with different failure modes, and fusing their incommensurable scores into one stable, explainable number is a harder problem than any single model. A bank building in-house typically reproduces one algorithm and stalls at explainability.
How does ThetaRay's AI meet SR 11-7 model risk expectations?
ThetaRay's models are grounded in peer-reviewed harmonic analysis for conceptual soundness, use feature attribution for outcomes analysis, and include automated drift detection for ongoing monitoring. Kaufman Rossin independently validated the AML Transaction Monitoring and OFAC Screening modules, finalized in August 2025.
How is Ray different from an LLM chatbot?
Ray is an orchestration layer that runs defined workflow steps, uses scoped data access under governance, and sits on the same engine as ThetaRay detection, so it can reason about why an alert fired. Every Ray investigation produces a policy-aligned narrative, a traceable logic trail and automatic audit logs.
How long did a Tier-1 bank take to deploy agentic AI in production?
A Tier-1 EU banking group reached production go-live with Ray in ~12 months, with the first capability delivered in ~3 months. The bank signed its Phase 2 expansion 16 days after go-live.